Emblaze.ca

Emblaze News

Latest announcements and updates.

Celine DiNova Campaign Site Refreshed for 2026

We kept the campaign’s familiar design while updating 2026 voter guidance, candidate images, and section contrast. The Basic Site made a fast, focused refresh possible across desktop and mobile.
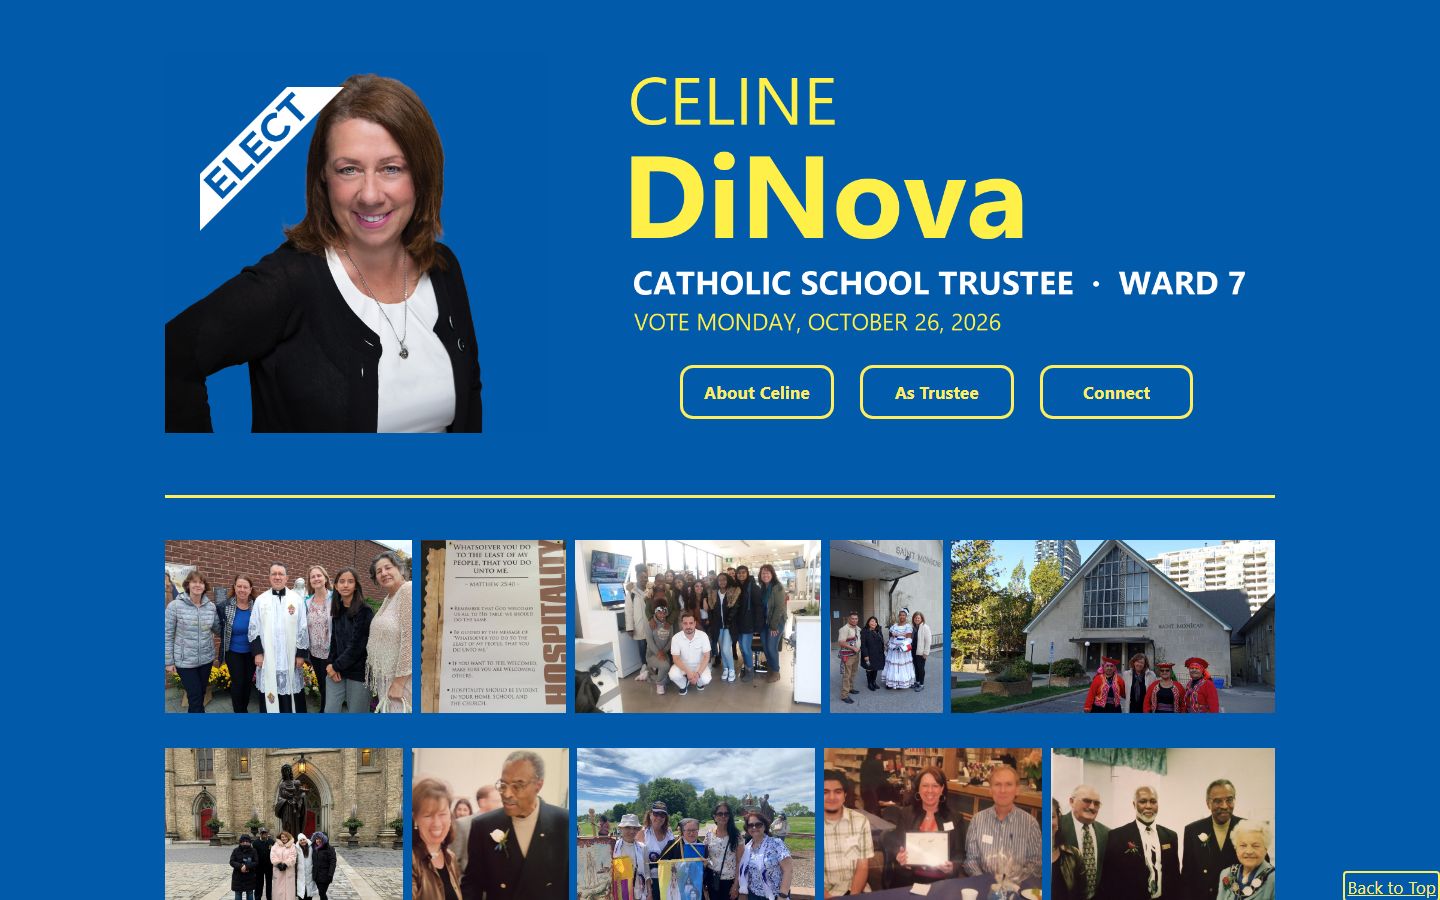
Celine DiNova campaign website

Emblaze refreshed Celine DiNova’s campaign site for the 2026 election, updating its content, images, and voter information while retaining the familiar design previously approved for the campaign.

We replaced the previous campaign’s time-sensitive material with current Ward 7 context and voting guidance. Updated candidate imagery and biography help visitors quickly understand Celine’s background and find official voting information. The familiar design remained in place, keeping the campaign recognizable to returning visitors.

We then reviewed the page on desktop and mobile. The endorsement area and advance-voting section received contrast improvements so important text reads clearly against its background. Image descriptions and section details were also refined as the new material was published.

This is the strength of a focused Basic Site during a campaign: content can be delivered quickly, checked in context, and adjusted as information changes without rebuilding the whole experience.

Visit Celine DiNova’s campaign site.

More news

Emblaze News: Critical PHP Security Release: What Website and Server Owners Need to Do
PHP released emergency fixes on October 21 for two critical engine flaws involving out-of-memory cleanup and use-after-free state across requests. This guide explains what EZCMS and WordPress owners should ask their host to verify, and gives Net Management operators a practical Webmin, terminal, Azure, AWS, and on-prem patch checklist. An October 23 PHP follow-up adds one temporary setting to review.

On October 21, 2026, PHP released emergency fixes for CVE-2026-109618 and CVE-2026-109619, two critical flaws that can allow unauthenticated remote code execution. The latter is the “use after free” issue: a worker can retain a pointer to memory from a completed request, then use that stale state in a later request. The first concerns out-of-memory cleanup during partial request initialization. PHP identifies all web-facing PHP installations as in scope and calls out Apache mod_php as the highest demonstrated risk.This is a PHP engine issue beneath both EZCMS and WordPress. Updating either application alone does not replace the PHP build used by the web server. The immediate job is to identify the PHP build actually serving each site, apply a fixed vendor build, restart workers, and verify the result. On October 23, PHP also advised a temporary setting for a separate, uncommon session upload progress path.

Read More
Emblaze News: S.V. La Costa Business Site Advances Its Product Workflow
For S.V. La Costa, clearer catalogue save feedback helps staff maintain product content. After an accepted contact or product enquiry, customers see a confirmation that can include a follow-up reference; if email notification is delayed, the page says so. These workflows give its Business Site practical utility beyond a product display.

Recent work on the S.V. La Costa Business Site improved product catalogue administration and the way customer enquiries are acknowledged.

Read More

Emblaze.Ca®Emblaze.Ca

Fire Solutions and Support for Information Technology

Contact

Use our contact page to request an email reply or call back.

Contact Emblaze

Visit

208-4800 Highway 7
Vaughan, ON. L4L 1H8